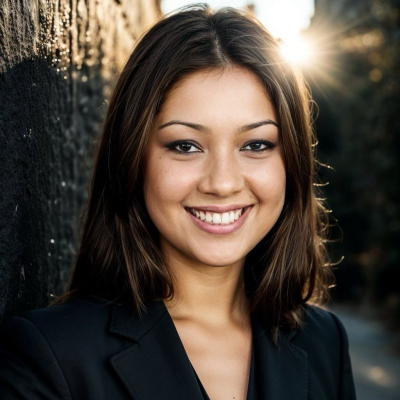
Nivedita Newar
Deputy CISO University of New South Wales
AI Infrastructure and Enterprise Systems Summit - Day 1
4:00 PM The Attack Surface Nobody Modelled: Securing AI Infrastructure at the Speed You're Deploying It
Most ANZ enterprises are deploying AI faster than they can secure the infrastructure underneath it, treating security as a retrofit rather than a design principle. This session takes a CISO's view of where that catches up with you: shadow AI tools running outside approved stacks, third-party model and vendor risk, and the expanded attack surface created by real-time data pipelines and API sprawl. A practitioner account of what a security-first AI infrastructure build actually requires, and what skipping it costs later.
Check out the incredible speaker line-up to see who will be joining Nivedita.
Download The Latest Agenda


